Cisco Sinkholes GozNym Banking Trojan Botnet
GozNym botnet included over 23,000 infected victims. The Cisco Talos team has announced today that they’ve successfully managed to sinkhole one of GozNym’s botnets and are in the process ofRead More →
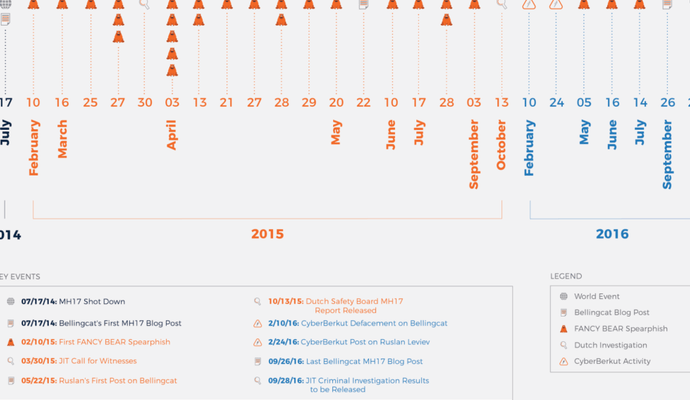
Researchers at the Bellingcat agency have been hit with spear phishing attacks and account takeover attempts while investigating flight MH17 crash. Once again cyber security experts warn of a newRead More →
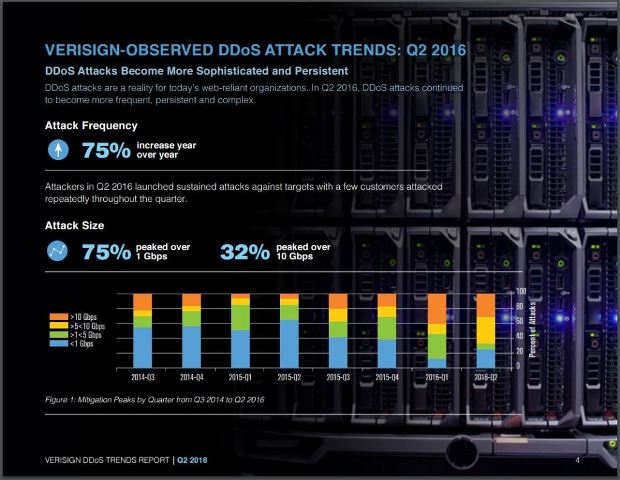
Once unthinkable, 1 terabit attacks may soon be the new normal. Last week, security news site KrebsOnSecurity went dark for more than 24 hours following what was believed to be aRead More →
Today we bring you Princess Locker; the ransomware only royalty could love. First discovered byMichael Gillespie, Princess Locker encrypts a victim’s data and then demands a hefty ransom amount ofRead More →
Unlock92 infections going under the radar. A ransomware variant that appeared in early July this year and was initially cracked and decrypted has quietly resurfaced in mid-August and has beenRead More →
Now, this first one isn’t such a huge issue as it would require physical proximity to the router, at the same time that the user is trying to do aRead More →
The hosting provider OVH continues to face massive DDoS attacks launched by a botnet composed at least of 150000 IoT devices. Last week, the hosting provider OVH faced 1Tbps DDoS attack,Read More →
Two years after its first version, osquery gets Windows port. Facebook’s insanely popular osquery project is now available for Windows after it was launched in 2014 with support for only MacRead More →
Ars reports from the Linux Security Summit—and finds much work that needs to be done. The Linux kernel today faces an unprecedented safety crisis. Much like when Ralph Nader famouslyRead More →
We recently observed Hancitor attacks against some of our FireEye Exploit Guard customers. The malicious document used to deliver the Hancitor executable was observed being distributed as an attachment inRead More →
Short Bytes: At its Ignite conference, Microsoft announced Windows Defender Application Guard for its Edge Browser. This technology will run Edge in a lightweight virtual machine, isolating it from theRead More →
PonyForx is a fork of the more popular Pony infostealer. A crook named Cronbot is currently selling a new malware variant on Russian underground hacking forums that appears to beRead More →
The Sofacy group, also known as APT28, Pawn Storm, Fancy Bear, and Sednit, continues to add to the variety of tools they use in attacks; in this case, targeting individualsRead More →
i-Dressup operators fail to fix bug that exposes up to 5.5 million credentials. A social hangout website for teenage girls has sprung a leak that’s exposing plaintext passwords protecting as manyRead More →
Ransomware in its various forms continues to make headlines as much for high-profile network disruptions as for the ubiquity of attacks among consumers. We recently noted the non-linear growth ofRead More →
Short Bytes: More and more things are getting connected to the internet. Apart from its advantages, it also raises a concern regarding these things becoming prone to hackers. A DARPA-ledRead More →
Internet relay chat (IRC) is a fundamentally primitive technology, a precursor to social networks, and, especially, chat services like Slack and Hipchat. Slack, in particular, has been quietly decimating IRCRead More →
ARMENIAN HACKERS LEAKED PERSONAL DETAILS OF GOVERNMENT OFFICIALS AND ALSO DEFACED EMBASSY SITES TO CELEBRATE 25 YEARS OF ARMENIAN INDEPENDENCE. Armenian hackers from Monte Melkonian Cyber Army (MMCA) have leaked a trove ofRead More →
According to the popular cyber security experts an unknown nation state actor may be running tests for taking down the entire internet infrastructure. What happens if someone shuts down the Internet?Read More →
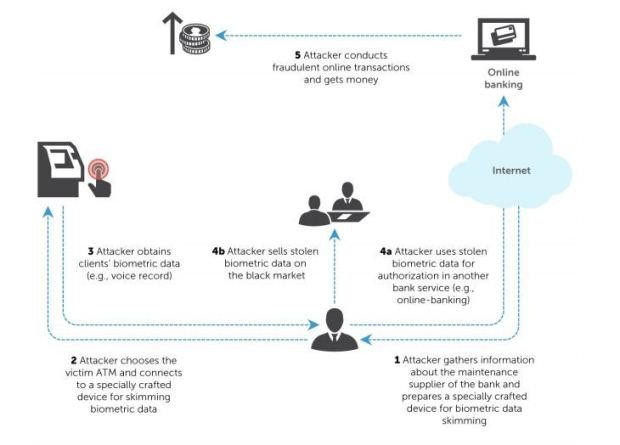
Kaspersky Lab presented an investigation on the future of ATM Biometric Skimmers and how cybercriminals could exploit them. A recent investigation by Kaspersky Labs reports that a number of undergroundRead More →