Former Twitter CEO Dick Costolo was hacked
OurMine, the same group that hacked Mark Zuckberg’s Pinterest and Twitter accounts, seems to be behind it. Even the former CEO of Twitter isn’t protected from the occasional security hack.Read More →
We found a new piece of mobile malware, Android/Trojan.Pawost, that’s using Google Talk to make malicious calls. As soon as the malicious app is opened, a blank Google Talk iconRead More →
Users are now prompted to update to the latest version. Apple is now blocking older versions of Adobe’s Flash Player because of security vulnerabilities that were patched in the most recentRead More →
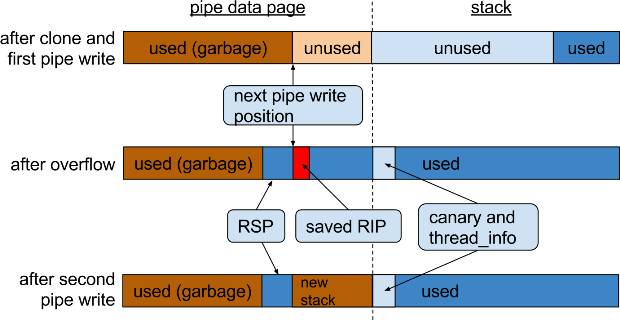
On June 1st, I reported an arbitrary recursion bug in the Linux kernel that can be triggered by a local user on Ubuntu if the system was installed with homeRead More →
Two mobile variants of Triada and Horde malware have been spotted in the wild by Check Point Software Technologies researchers who warn the latest samples have adopted dangerous new techniques includingRead More →
An unnamed hacker hacked the video conferencing software used by the Quebec Liberal Party and shared the news with the media. Politicians are a privileged target of hackers, in manyRead More →
The employee tried to cash in by stealing and selling the data of up to 1.5 million Czech customers. T-Mobile’s arm in the Czech Republic has uncovered an employee’s intentionsRead More →
Incident seems to be another ATO (account takeover) attack.GoToMyPC decided to reset user passwords after attackers tried to hack into customer accounts over the weekend using what the company callsRead More →
Lost info includes names, addresses, numbers and security codes. Acer’s insecure customer database spilled people’s personal information – including full payment card numbers – into hackers’ hands for more than aRead More →
Selfrando is an alternative to ASLR memory randomization. At the start of June, the Tor Project released version 6.5a1 of the Tor Browser, but compared to previous releases, this one alsoRead More →
DAO had just raised $150 million in record crowdfunding effort. A futuristic technology experiment appears to have fallen prey to a common technological risk, as operators of a new investment fundRead More →
Today the federal Government Accountability Office (GAO) finally published its exhaustive report on the FBI’s face recognition capabilities. The takeaway: FBI has access to hundreds of millions more photos thanRead More →
The Pirate Bay cofounder Peter Sunde says ‘Bullying is the new Black’ after being fined $395,000 in damages to media companies The Pirate Bay co-founder Peter Sunde has been orderedRead More →
How do companies regardless of size and industry prepare for ransomware attacks? A recent study revealed that businesses are considering saving up Bitcoins, just in case they get hit by theseRead More →
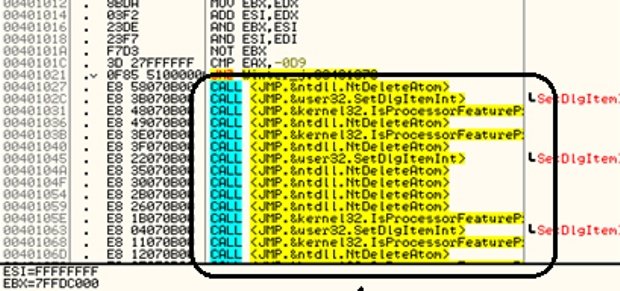
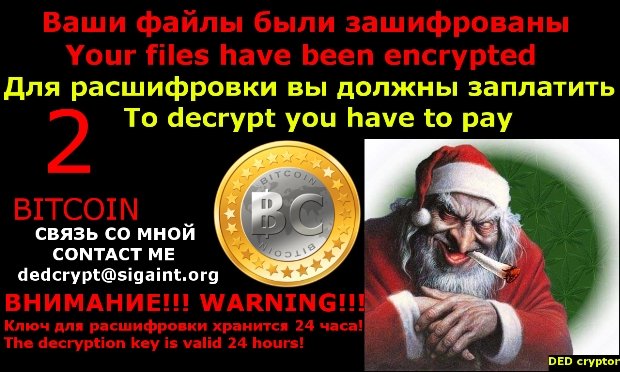
A new EDA2 ransomware was discovered by Michael Gillespie called Ded Cryptor. This ransomware has been around for quite a while and targets both Russian and English speaking victims. When installed, the victimsRead More →
Python’s built-in URL library (“urllib2” in 2.x and “urllib” in 3.x) is vulnerable to protocol stream injection attacks (a.k.a. “smuggling” attacks) via the http scheme. If an attacker could convinceRead More →
Users of the TeamViewer remote-access service have beencomplaining in recent weeks about how their systems have been hacked into, unauthorized purchases made on their cards, their bank accounts emptied. Initially itRead More →
Intel x86 CPUs Come with a Secret Backdoor That Nobody Can Touch or Disable. Hardware security expert Damien Zammit says that recent Intel x86 CPUs come with a secret subsystemRead More →
Repository’s own account data not breached, affected passwords reset. On June 14, someone using what appears to have been a list of e-mail addresses and passwords obtained from the breach ofRead More →
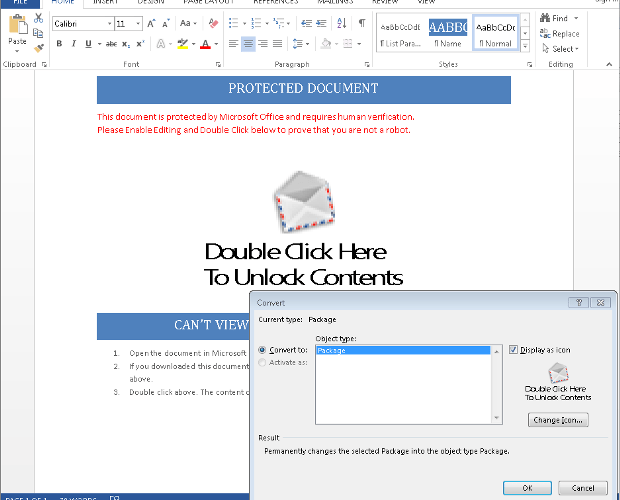
Sysadmins should disable OLE object execution. Malware coders have found a macro-like infection method that abuses the Microsoft Object Linking and Embedding (OLE) system to trick users into running malicious scripts.Read More →