Brazilian banking Trojans meet PowerShell
2016-08-20
Crooks are always creating new ways to improve the malware they use to target bank accounts, and now Brazilian bad guys have made an important addition to their arsenal: theRead More →
Crooks are always creating new ways to improve the malware they use to target bank accounts, and now Brazilian bad guys have made an important addition to their arsenal: theRead More →
Researcher claims that iPhone’s ‘Live Photos’ can be used to hack 2 banks apps. In a shocking discovery, a researcher found that 2 banks’ mobile phone apps were susceptible to hack,Read More →
Trojan targets CMS platforms running on Linux servers. What initially looked like a string of Drupal sites infected with ransomware (that didn’t work properly) now looks like a professional cybercrime operationRead More →
Exploit against Cisco’s PIX line of firewalls remotely extracted crypto keys. In a revelation that shows how the National Security Agency was able to systematically spy on many Cisco Systems customersRead More →
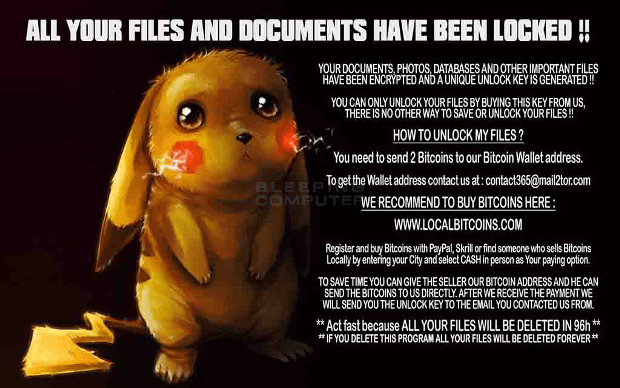
A new ransomware called DetoxCrypto has been discovered by MalwareHunterTeam that is currently being distributed under two different variants. The first variant looks like a generic ransomware but contains the interestingRead More →
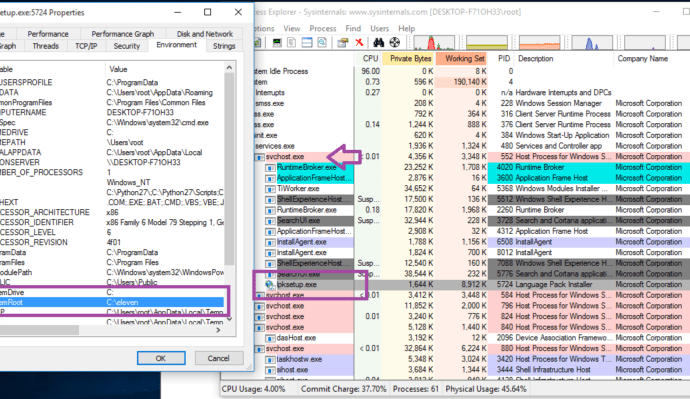
Microsoft delays fixing the reported issue. enSilo senior security researcher Yotam Gottesman has discovered a simple method of bypassing the Windows User Account Control (UAC) mechanism that affects all supported WindowsRead More →
Bitcoin traders have been warned that the upcoming Bitcoin Core software release will become a top target for well-funded hacking groups. Bitcoin.org has warned users to be aware that theRead More →
Clothing store chain Eddie Bauer said today it has detected and removed malicious software from point-of-sale systems at all of its 350+ stores in North America, and that credit and debitRead More →
New versions of Libgcrypt and Gnu Privacy Guard (GnuPG or GPG) released on Wednesday include security fixes for vulnerabilities discovered in the mixing functions of the Libgcrypt random number generator.Read More →
Crooks hijack the FSociety brand for a lame ransomware. Fans of the Mr. Robot TV show would be glad to know that real-life crooks are taking inspiration from the TV series,Read More →
Chrome, Firefox and likely other major browsers are afflicted by a vulnerability that allows attackers to spoof URLs in the address bar. While Mozilla said it has patched the flawRead More →
The smart plug can act as a conduit not just for electricity — but for cyberattacks. Researchers have discovered critical security flaws in connected smart plugs which can give attackers accessRead More →
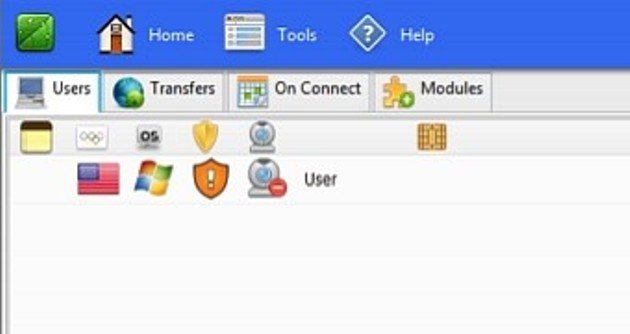
The Adwind Remote Access Trojan (RAT) is a popular Java-based backdoor capable of infecting Windows, Linux, Mac OS and Android operating systems. Its cross-platform nature, elaborate backdoor features, and relativelyRead More →
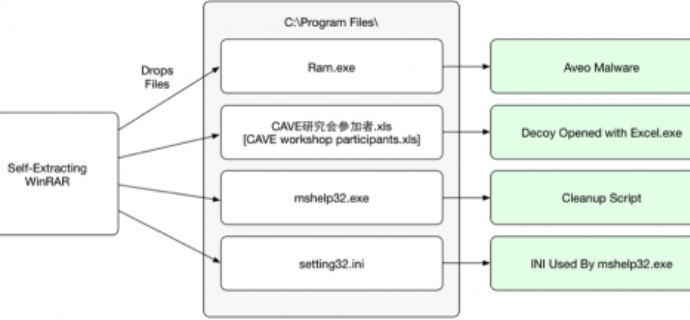
Palo Alto Networks has identified a malware family known as ‘Aveo’ that is being used to target Japanese speaking users. The ‘Aveo’ malware name comes from an embedded debug stringRead More →
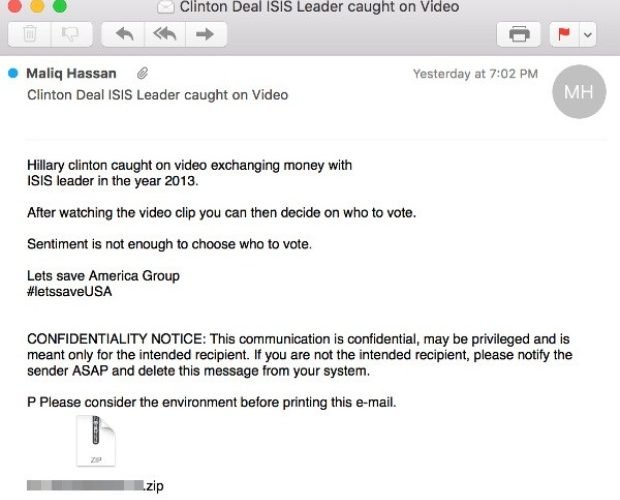
Malicious attachment contains Adwind cross-platform remote access Trojan. Cybercriminals are using clickbait, promising a video showing Democratic Party presidential nominee Hillary Clinton exchanging money with an ISIS leader, in order toRead More →
If the malware found any German financial apps installed in the device, it would show a fake page asking for credentials of that particular institution. Unaware that the login pageRead More →
Former NSA security scientist concurs exposure by “Equation Group” connected to DNC leak. Two former employees of the National Security Agency—including exiled whistleblower Edward Snowden—are speculating that Monday’s leak of whatRead More →
Many people don’t truly understand the extent to which computers control in the modern world. Everything from stoplights at busy intersections to power plants have automated systems, and for goodRead More →
Proofpoint researchers originally discovered the Panda Banker malware in February, 2016 [1]. At the time, it was being distributed via both targeted email campaigns and exploit kits (EKs). The instanceRead More →
Crooks also delivering keyloggers and password stealers. A new trojan called BackDoor.TeamViewerENT.1 is using parts of the legitimate TeamViewer application to allow crooks to spy on infected systems. The concept isRead More →