Tips on Getting into Cybersecurity Career Path
2020-03-11
Cybersecurity experts have a lot of power. From being able to hack a Tesla Model X to secure a business’s network, their immense skills are in demand. Online security hasRead More →
Cybersecurity experts have a lot of power. From being able to hack a Tesla Model X to secure a business’s network, their immense skills are in demand. Online security hasRead More →
A young college student managed to hack the card system of some restaurants in Singapore to get free food, drinks and cigarettes. According to the participants of information security training,Read More →
Reports of security flaws in modern processors have become very common. The instructor in a prestigious firm’s hacking course, as well as other researchers, have revealed a hardware and firmwareRead More →
Reports of ransomware attack incidents grew considerably as of the second half of 2019, and apparently the trend has continued. A cloud computing security firm has reported an infection withRead More →
Multiple information security training firms, researchers and instructors recently reported the finding of a serious vulnerability in more than 600 subdomains belonging to Microsoft; the successful exploitation of this flawRead More →
A recent report by participants of a cyber security course mentions the presence of a flaw that makes it possible to extract sensitive information from AMD processors, manipulating the L1DRead More →
Members of a hacking course discovered that Urllib3, a popular Python HTTP client, could be exposed to the exploitation of a recently discovered denial of service (DoS) vulnerability. It isRead More →
In this generation, everyone is interested in watching all types of movies sitting at one place, for this we have different providers like Amazon Prime, Netflix. Now days many peopleRead More →
Introduction “Extended XSS Search” is based on initial ideas of XSSfinder. XSS is also called a Cross Site Scripting, it is a type of security vulnerability found in web application.Read More →
A security alert, issued by instructors in the US-CERT hacking course, has been revealed, related to a dangerous remote execution flaw that has been present for nearly 18 years inRead More →
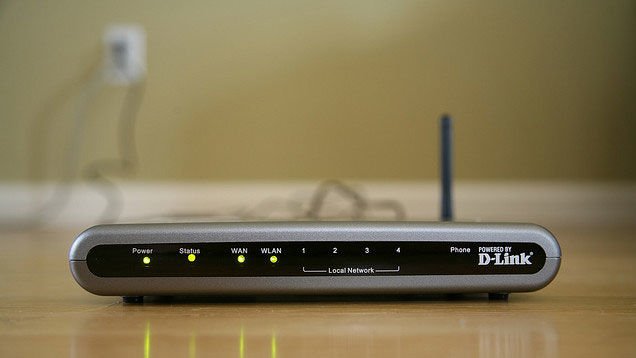
Recently Gianluca Pacchiella, researcher and specialist of a cyber security course published a blog post referring to CVE-2020-9544, a zero-day vulnerability involving the D-Link router DSL-2640B. “I did a securityRead More →
A cloud computing security firm has revealed the discovery of a critical zero-day vulnerability in one of the enterprise products of tech firm Zoho; according to the report, this flawRead More →
Although hackers often achieve to commit their crimes without leaving a trace, there are cases when authorities manage to identify them with relative ease. After taking a hacking course, anRead More →
Participants and instructors of information security training launched a software tool designed to bypass deep packet inspection (DPI). SymTCP is an open source tool for detecting subtle discrepancies between twoRead More →
For a couple of years now, cybersecurity firms, manufacturers and mainly car owners with keyless opening and start system have reported multiple incidents of “relay attacks”, which consist of theRead More →
Introduction In this smart world everything is connected to the internet, we can find hidden details using a google search engine. Google is used for everything and using this sameRead More →
An ethical hacking team has conducted a deep research on the major virtual private network (VPN) tools available on Google Play Store, discovering the presence of multiple security vulnerabilities inRead More →
Security products and solutions must be constantly updated as they are not exempt from exposure to exploitable vulnerabilities. According to a report from information security experts, the developers of theRead More →
Typo squatting is very common among technology users, so threat actors seek to take advantage of these oversights, creating websites of names similar to others by changing only a fewRead More →
Web application security specialists reported the finding of a security flaw in the CAA authorization code of the Let’s Encrypt Certification Authority (CA); the vulnerability creates a time window inRead More →